Topic Introduction
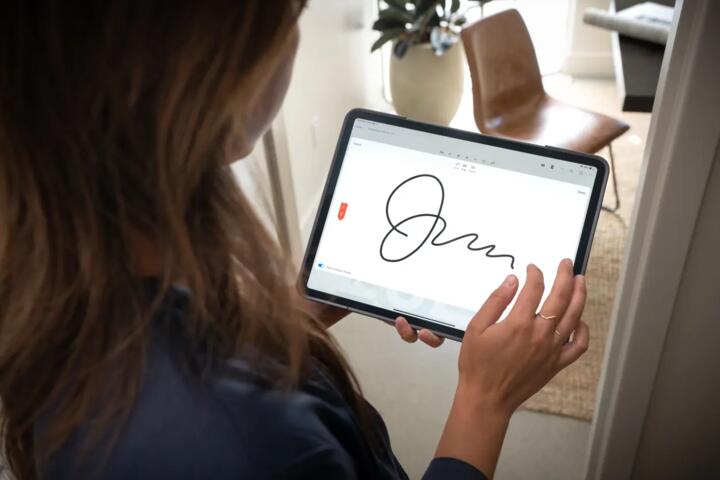
E-signature tools convert a paper signing step into an electronic workflow that records who signed, when they signed, and what content they signed. In practice, that means a user receives a document link, reviews the PDF (or another file type), and applies a signature method such as typing a name, drawing a signature, or using a certificate-based digital signature.
Most tools also generate an audit trail: timestamps, signer identity signals, IP address or device metadata (depending on the vendor), and a record of document versions. For example, a clinic might send a consent form for a procedure, collect signatures from a patient and a witness, and then store a final signed PDF plus the audit log for later review.
Legal enforceability depends on jurisdiction and on whether the workflow meets the requirements for electronic records and signatures. In the United States, the Electronic Signatures in Global and National Commerce Act (ESIGN) and the Uniform Electronic Transactions Act (UETA) generally support enforceability when parties consent to electronic records and signatures and the method is reliable for the transaction.
Main Problems Or Pain Points
People often treat e-signature as a visual effect—an image of a signature—while the legal and operational value comes from the evidence trail and the controls around document integrity.
One common mistake is choosing a tool that supports signing but not the surrounding governance. If the tool cannot lock the document after signing, or if it allows edits after signature without a new signing event, the audit trail becomes harder to defend. Another frequent issue is identity verification that is too weak for the risk level. A typed name with no additional checks may be acceptable for low-risk internal paperwork, yet it can be a poor fit for sensitive consents.
Supporting technologies also drive outcomes. A typical workflow depends on PDF rendering, hashing of document content, signer authentication, and storage of the final signed artifact. Some tools use cryptographic hashing to detect changes; others rely more on workflow controls. When vendors describe “tamper-evident” records, the practical question is whether the signed document and audit trail are bound together and whether the system preserves the exact signed content.
Another pain point is integration friction. Many organizations need e-signature to connect with document management systems, patient portals, or case management tools. If the integration is limited to manual exports, staff time rises and errors creep in. I’ve seen teams lose hours because the signed PDF exported from one system didn’t match the version referenced in the audit report—an issue that shows up only after a dispute or audit.
Solutions And Advice
Verify Legal Signature Level
Start by mapping your use case to the legal category you need. In the EU, eIDAS distinguishes between simple electronic signatures, advanced electronic signatures, and qualified electronic signatures. In the US, ESIGN and UETA focus on consent and reliability rather than a single “tier,” but your workflow still needs to show that the signature process is attributable to the signer and that the record is retained.
Practical step: write down who signs (patient, clinician, guardian), what they sign (consent, policy acknowledgment, release), and what evidence you must retain. Then compare vendor documentation on identity verification, audit trail contents, and whether the tool supports certificate-based digital signatures or advanced signature profiles.
Test Audit Trail And Integrity
Before purchasing at scale, run a controlled test with a realistic document set. Create a test envelope, sign with the intended method, download the final signed PDF, and inspect what the audit report claims. Check whether the signed PDF includes the final content and whether the audit trail references the same document hash or version identifier.
Look for evidence that the system prevents silent changes. Some tools lock the signed document and require a new signing event for modifications; others allow certain metadata edits. A minor aside from a recent evaluation: one vendor’s audit report listed “document hash” but the exported PDF lacked the corresponding identifier, which made reconciliation harder for our internal reviewers.
Outcome target: within 30–60 minutes per tool, you should confirm that (1) the signer sees the exact content they sign, (2) the final artifact is reproducible, and (3) the audit trail can be exported or accessed later without breaking the chain of evidence.
Match Identity Checks To Risk
Identity verification methods vary widely. Some tools rely on email link plus basic authentication; others add knowledge-based checks, SMS codes, or third-party identity verification. For healthcare-related consents, the risk profile often justifies stronger checks than a simple email link, especially when signatures affect clinical decisions or legal rights.
Practical step: classify documents by sensitivity and consequence. A general policy acknowledgment may tolerate lighter verification, while a consent for a procedure or a release of information typically needs stronger assurance. Then compare vendor options for signer authentication, including whether the tool supports role-based signing, witness flows, or multi-signer sequencing.
Outcome target: you should reduce “wrong person signed” risk by aligning verification strength with document consequence. If a vendor offers only one verification method across all plans, that constraint matters.
Plan Storage, Retention, And Access
E-signature tools store signed documents and audit logs, but retention policies depend on the vendor plan and your configuration. Ask how long signed artifacts remain accessible, whether you can export them in bulk, and whether audit logs remain available after account changes. Also confirm how the tool handles re-sends, cancellations, and partial signing.
Practical step: define your retention requirement and test export. For example, if your organization retains consent records for multiple years, verify that the tool’s export format remains usable and that the audit trail remains readable. Some tools export a “certificate of completion” plus the signed PDF; others provide a JSON or CSV audit export.
Case Examples
Clinic Consent Workflow
A small outpatient clinic needs patient and witness signatures for procedure consents. The clinic tests three tools and discovers that one tool’s audit trail records signer IP and timestamp but does not clearly bind the witness signature to the exact final PDF version. Another tool binds the signed content and provides an exportable audit report, but its identity check is limited to email link authentication.
The clinic chooses the tool that offers stronger identity options and a clear integrity story, then configures a two-step signing sequence: patient signs first, witness signs second, and the system locks the document after each signing event. Staff record the final signed PDF and audit report in the clinic’s document repository.
HR Policy Acknowledgment
A mid-sized employer collects employee acknowledgments for updated policies. The organization uses an e-signature tool with simple authentication because the documents do not affect clinical rights and the main goal is proof of receipt. The team still tests audit trail export and confirms that the signed PDF matches the version shown to the employee.
To reduce errors, the employer standardizes the envelope template and uses reminders only for incomplete signatures. After a month, they review completion rates and find that most delays come from employees ignoring email notifications, not from signing failures. The team then adjusts the reminder schedule and adds a calendar reminder in their HR system.
Comparison Table Or Checklist
Use this checklist to compare tools without relying on marketing claims. The table below uses common evaluation categories; exact feature availability varies by plan and region.
| Evaluation Parameter | What To Look For | Why It Matters | How To Test |
|---|---|---|---|
| Signature Type | Simple vs advanced vs certificate-based | Determines legal assurance level | Check vendor docs and run a signing test |
| Audit Trail Contents | Timestamps, signer identity signals, document integrity references | Supports dispute resolution | Export audit report and compare to signed PDF |
| Document Locking | Prevents edits after signing or records new signatures | Preserves integrity of the signed content | Try a post-sign modification and observe behavior |
| Identity Verification | Email link, SMS, knowledge checks, third-party verification | Reduces “wrong signer” risk | Confirm available methods for your plan |
| Retention And Export | Access duration, bulk export formats, audit log availability | Supports long-term recordkeeping | Request sample exports; verify readability |
| Workflow Controls | Multi-signer order, witness support, reminders | Reduces operational errors | Run a multi-signer test with reminders |
Step-by-step checklist for a purchase decision:
- List your top 5 document types and the signer roles for each.
- Write the evidence you need: attribution, integrity, and retention duration.
- Run a signing test with the exact PDF you plan to use and download the final artifact.
- Compare audit trail exports across tools and confirm the signed content matches the audit report.
- Verify identity verification options for your plan and region.
- Confirm retention and export behavior if the subscription ends.
- Check integration needs and test a real workflow end-to-end.
Common Mistakes
Teams often pilot a tool with a single document and then assume the same results apply to all document types. PDF forms with embedded fields, scanned images, or multi-page consent add edge cases that affect rendering and signature placement.
Another mistake is ignoring signer experience details. If the signing flow requires repeated logins or fails on mobile browsers, completion rates drop and staff start “workarounds” that weaken the audit trail.
People also underestimate version control. If a document template changes after an envelope is created, some systems keep the old content while others update the envelope. That mismatch becomes a problem when someone later claims they signed a different version.
Some organizations store only the signed PDF and discard the audit report. That choice can hurt during disputes because the audit report often contains the evidence fields that explain what happened.
FAQ
Do E-Signatures Replace Wet Signatures?
E-signatures can replace wet signatures for many transactions when the parties consent to electronic records and signatures and the method is reliable for the transaction. Some regulated contexts may require advanced or qualified signatures, depending on jurisdiction and contract terms.
What Proof Does An Audit Trail Include?
An audit trail typically includes timestamps, signer identity signals (such as authentication method), document version or hash references, and completion status. The exact fields vary by vendor and plan, so you should export a sample audit report and review it.
Can Signed Documents Be Edited After Signing?
Many systems lock the signed content after signing or require a new signing event for changes. You should test post-sign behavior by attempting a modification and confirming what the system records in the audit trail.
How Do Identity Checks Affect Legal Risk?
Stronger identity verification reduces the chance that someone else signs in the signer’s place. Legal enforceability still depends on jurisdiction and consent, but weak verification can weaken attribution arguments in disputes.
What Should I Verify Before Choosing A Tool?
Confirm signature type support, audit trail exportability, document integrity behavior, retention duration, and identity verification options for your plan. Then run an end-to-end test using your real document templates and signer roles.
Author's Insight
E-signature tools differ less in the visible signature and more in how they bind signed content to evidence. A defensible workflow depends on audit trail quality, document integrity controls, and retention/export behavior over time.
When evaluating vendors, treat documentation as a starting point and validate with a test envelope that matches your actual documents and signer roles. If the audit report cannot be reconciled with the downloaded signed PDF, the system will create friction during compliance review.
Legal requirements vary by jurisdiction and contract language, so the safest approach is to align the tool’s signature category and identity checks with the risk level of each document type.
Key Takeaways
- Compare e-signature tools by evidence and controls, not by signature appearance.
- Test that the signed PDF and audit trail match the same document version or integrity reference.
- Align identity verification strength with the consequence of the signed document.
- Verify retention and export behavior so signed records remain usable after subscription changes.